Bylines should describe who is accountable for the work.
DKCISSP uses an organizational newsroom byline for automated and multi-source coverage, and a named byline for directly authored analysis and opinion.
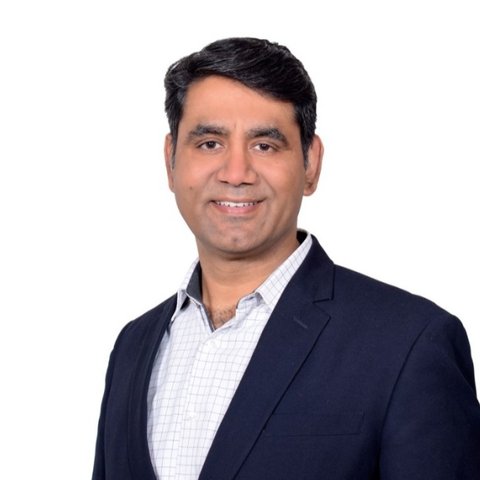
Deepak Kumar, CISSP
Enterprise security leader, 20 years
Deepak has spent two decades in enterprise security, working across governance, cyber defense, risk and compliance, third-party risk, and audits against frameworks such as SOC 2, ISO 27001 and GDPR.
He also works on the AI side of security, including AI governance and applying AI to make security assurance more continuous.
He started in IT operations two decades ago, which is why he leads security through organizational change rather than around it.
He is CISSP, CISA, CEH and OSCP certified, an ISO 27001 Lead Auditor, and holds cloud security architecture certifications across AWS, Microsoft and Google Cloud.
LinkedIn →DKCISSP Newsroom
Automated source collection, event aggregation and standard defensive-context articles are published under the DKCISSP Newsroom identity. This avoids implying that a named individual personally wrote or reviewed an automated item when that is not the case.
Named authors
When a person directly authors substantial analysis, research or commentary, a named byline is used with the author profile above. Opinion or analysis is labeled as such and kept distinguishable from factual news reporting.
Accountability
Regardless of byline, source provenance, correction standards and editorial policy apply to the published item. A byline does not substitute for evidence, and source references remain available for verification.