Cloud & IdentityIncident4h ago · 1 source
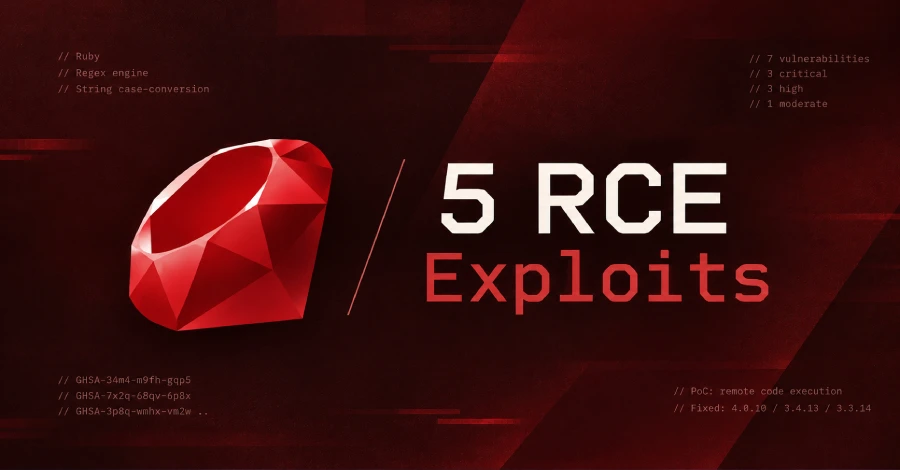
Ruby has released fixes for seven memory-safety vulnerabilities, five of which have proof-of-concept exploits that could lead to remote code execution.
VulnerabilitiesIncident5h ago · 2 sources
China-linked hackers exploited VMware vulnerabilities to gain access and reduce audit visibility.
AI SecurityIncident5h ago · 1 source
Researchers found that AI agents retrained on prompt injection attacks became easier to hijack, raising concerns about attack tool effectiveness.
Threat ResearchIncident5h ago · 1 source
Security teams should consider retiring vanity dashboards that do not provide actionable insights, according to an OT security architect.
AI SecurityIncident6h ago · 1 source
Postman found that many organizations using AI agents lack adequate security measures for their APIs, raising concerns over unauthorized access.
VulnerabilitiesIncident6h ago · 1 source
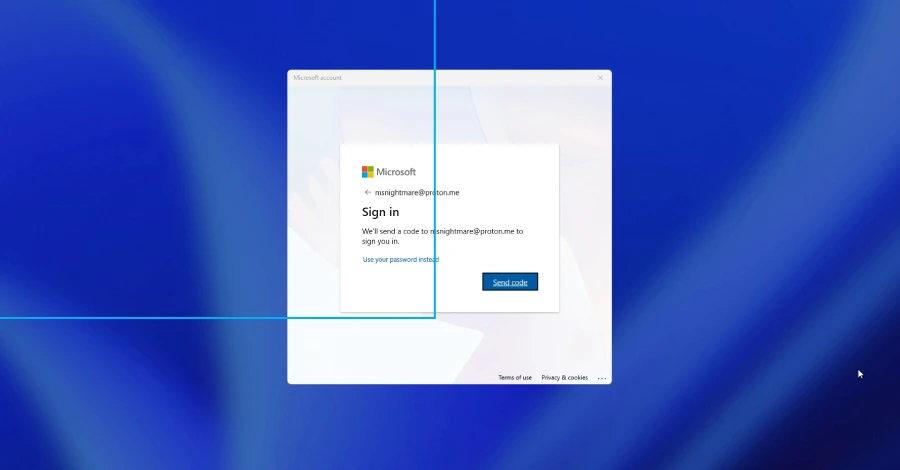
A newly disclosed unpatched zero-day technique called FastUnlock lets someone with physical access to a locked Windows computer start programs without signing in.
Cyber AttacksIncident6h ago · 1 source
A survey reveals many CIOs and CISOs lack quick access to critical network infrastructure during outages, impacting recovery efforts.
VulnerabilitiesIncident9h ago · 2 sources
A critical flaw in VMware vCenter lets an attacker with network access bypass authentication and gain unauthorized access to the system, Broadcom, which owns VMware, said in an advisory published today.
Cyber AttacksIncident11h ago · 1 source
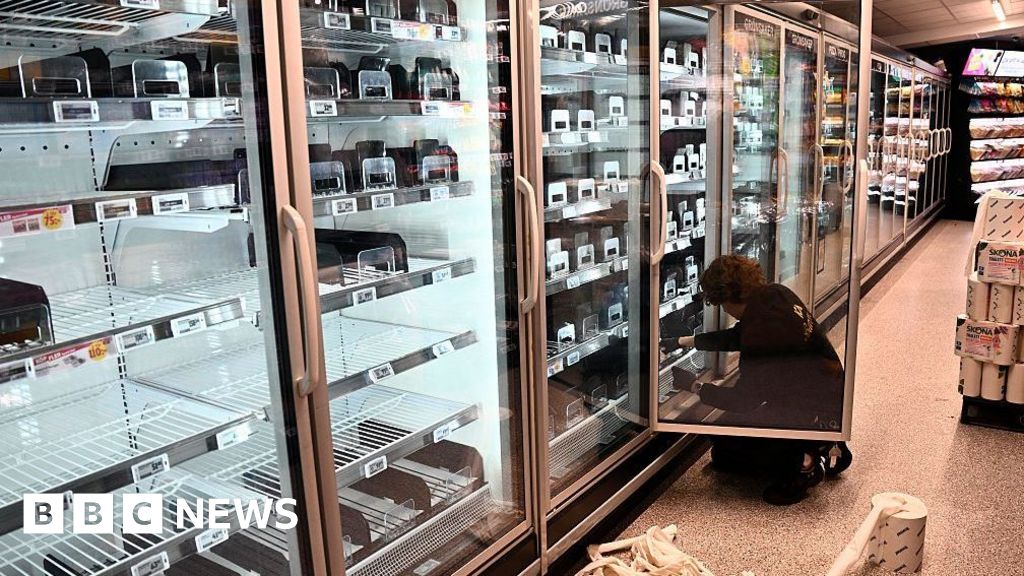
A covert cybersecurity operation has secured thousands of refrigeration devices in the UK from potential hacking threats, following recent cyber-attacks in Europe.
Threat ResearchIncident12h ago · 1 source
Google will extend Android developer verification to every country starting in January 2027, a check that already applies at participating app stores in four countries.
Cloud & IdentityIncident16h ago · 1 source
FBI has taken action against ThreatsDay GPT-6.2 Jailbreak, according to the latest reporting on the case.
VulnerabilitiesIncident17h ago · 1 source
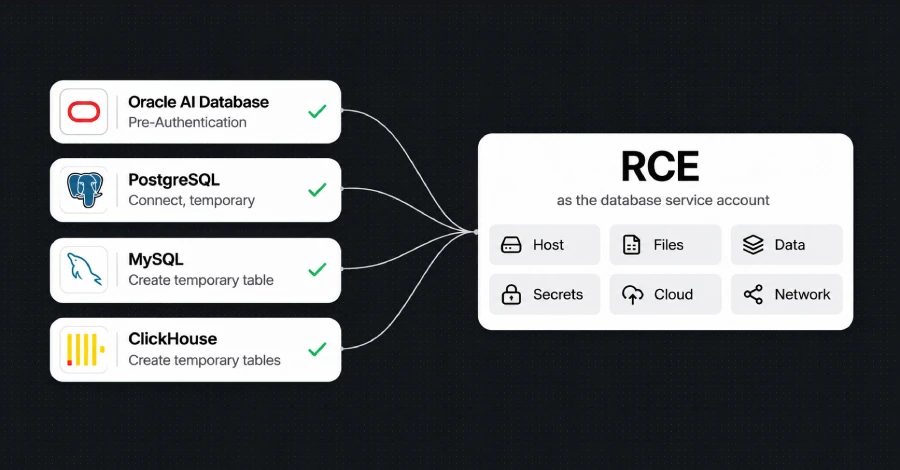
A researcher has demonstrated remote code execution exploits affecting PostgreSQL, MySQL, and Oracle, highlighting vulnerabilities in low-privilege database accounts.
VulnerabilitiesIncident17h ago · 2 sources
F5 has patched five critical vulnerabilities in NGINX, including a flaw that can lead to remote code execution.
Threat ResearchIncident19h ago · 1 source
The Dutch privacy watchdog advises against purchasing smart glasses due to serious safety and privacy concerns.
Cloud & IdentityIncident20h ago · 2 sources
PHP maintainers announced critical vulnerabilities affecting all supported versions, with fixes expected on November 19.
Threat ResearchIncident20h ago · 1 source
PHP 8.6 has been released, introducing several new features and changes to improve coding practices.
Threat ResearchIncident20h ago · 1 source
Railway disclosed unauthorized access to customer environment variables, urging credential rotation.
Data BreachesIncident21h ago · 4 sources
A Russian cyberespionage group used compromised cloud accounts to launch phishing attacks against new targets, Google Threat Intelligence Group found.
VulnerabilitiesIncident21h ago · 1 source
Drupal has patched a critical vulnerability that could allow unauthenticated attackers to take control of sites using its installer.
VulnerabilitiesIncident21h ago · 1 source
A new detection method for timeroasting has been developed, focusing on monitoring UDP traffic to identify potential password vulnerabilities in Windows systems.
VulnerabilitiesIncident21h ago · 3 sources
CISA warns of a critical Java vulnerability, CVE-2026-114938, allowing remote code execution, urging immediate patching by affected organizations.
VulnerabilitiesIncident22h ago · 1 source
Puppet is currently under active attack due to a flaw that enables unauthorized code execution, elevating this situation beyond a typical disclosure.
Cloud & IdentityIncident22h ago · 2 sources
Two releases of Microsoft’s official agent-framework package on the Python Package Index (PyPI) carried code that steals cloud and CI/CD credentials from developers’ systems.
Policy23h ago · 1 source
GTA frenzy has been convicted or has pleaded guilty in a case brought by law enforcement.

Threat ResearchIncident23h ago · 3 sources
GitLab's Duo Agent Platform has doubled its performance per GitLab Credit, enhancing efficiency for users.
RansomwareIncident1d ago · 2 sources
CISA has added four vulnerabilities to its Known Exploited Vulnerabilities catalog, highlighting active exploitation linked to various attacks.
Cyber AttacksIncident1d ago · 1 source
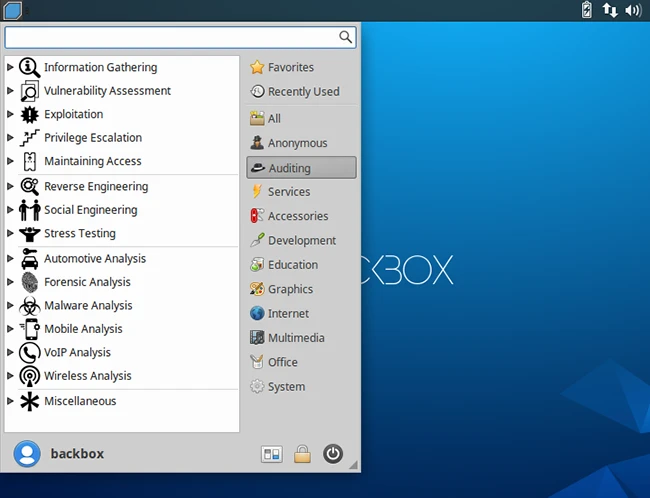
BackBox Linux 10 introduces new tools and enhanced features for penetration testing, including support for Ubuntu 26.04.
Threat ResearchIncident1d ago · 1 source
SonicWall has declared Gen 6 firewalls obsolete, urging immediate replacements as they pose a significant security risk.
AI Security1d ago · 1 source
Palo Alto Networks is acquiring Applied Compute for $4.5 billion to enhance AI security solutions.
VulnerabilitiesIncident1d ago · 1 source
Scammers exploit the anticipation for GTA 6 to steal credentials and funds through deceptive schemes.
Ransomware1d ago · 1 source
Ukraine has been convicted or has pleaded guilty in a case brought by FBI.
Data BreachesIncident1d ago · 1 source
N-able confirmed unauthorized access to its Mail Assure and Spam Experts Hosted Cloud, disrupting email security management.
Cyber AttacksIncident1d ago · 1 source
A new variant of EggStreme malware has been developed by a suspected Chinese APT group, enhancing its evasion tactics against security tools targeting government organizations.
Threat ResearchIncident1d ago · 1 source
The US has launched a new unit to prevent scammers from accessing victims' funds through private partnerships.
Cyber AttacksIncident1d ago · 1 source
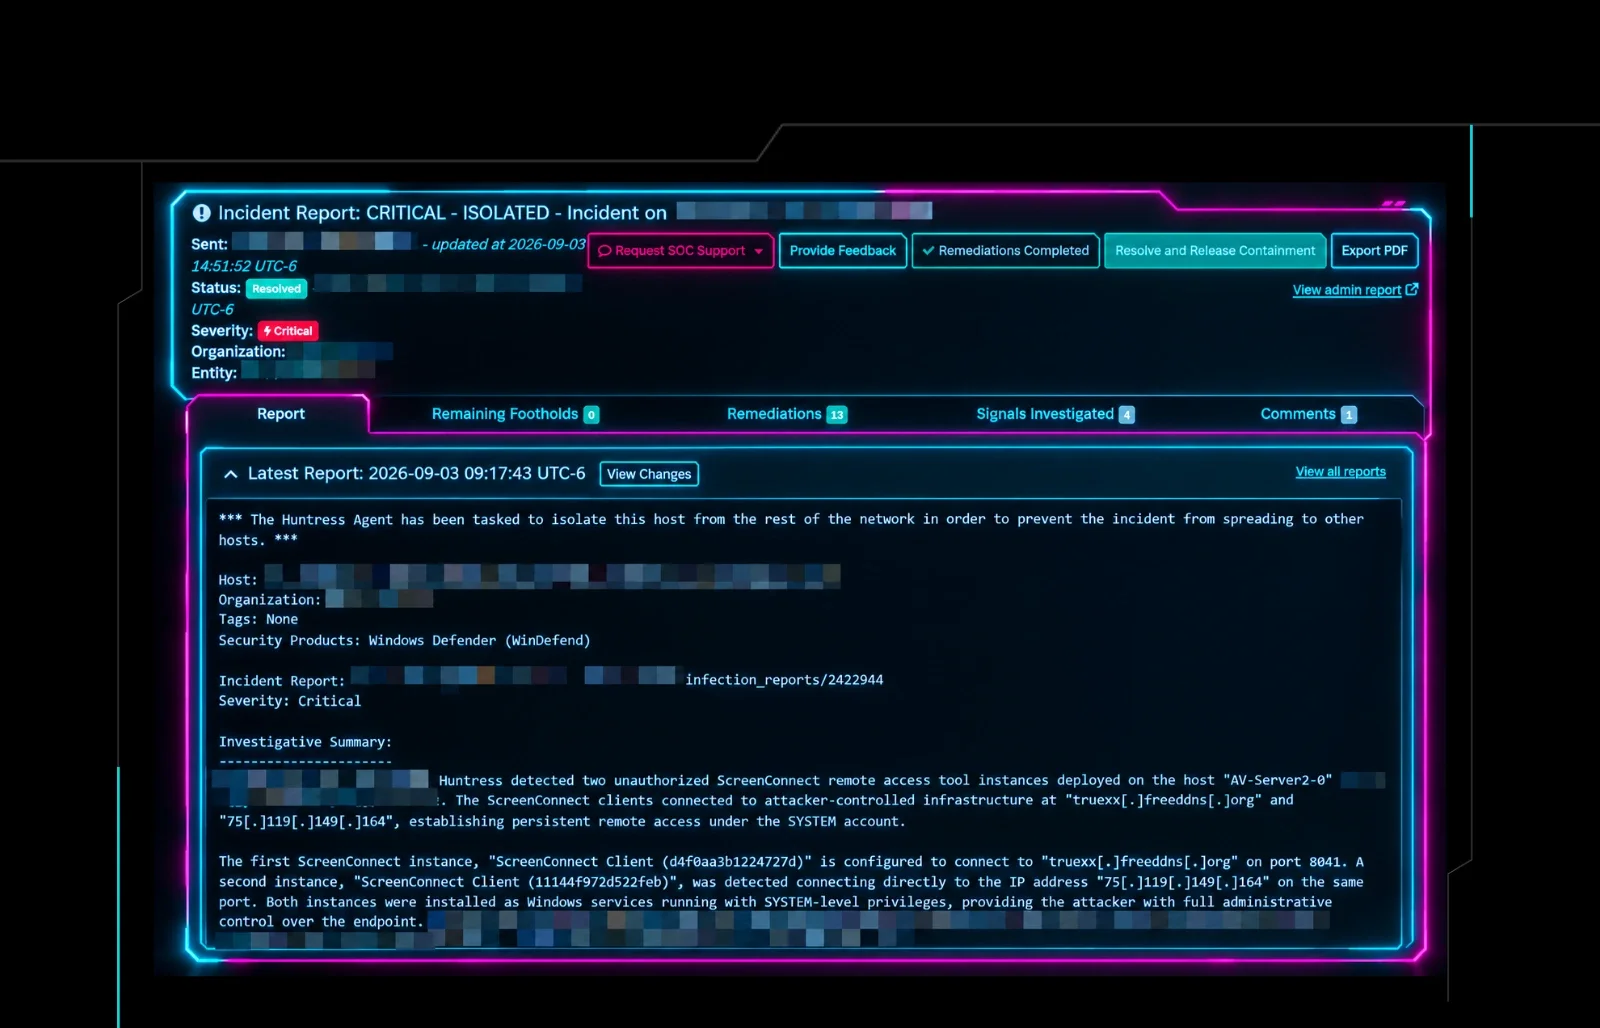
A managed service provider faced significant downtime after a cyberattack compromised their remote monitoring tools.
Threat ResearchIncident1d ago · 1 source
Consumer gadgets, including game consoles and Teslas, are improperly connected to production networks in critical infrastructure settings, raising cybersecurity concerns.
AI SecurityIncident1d ago · 1 source
AI agents built by employees often use their creator's credentials, raising security concerns.
Cyber AttacksIncident1d ago · 1 source
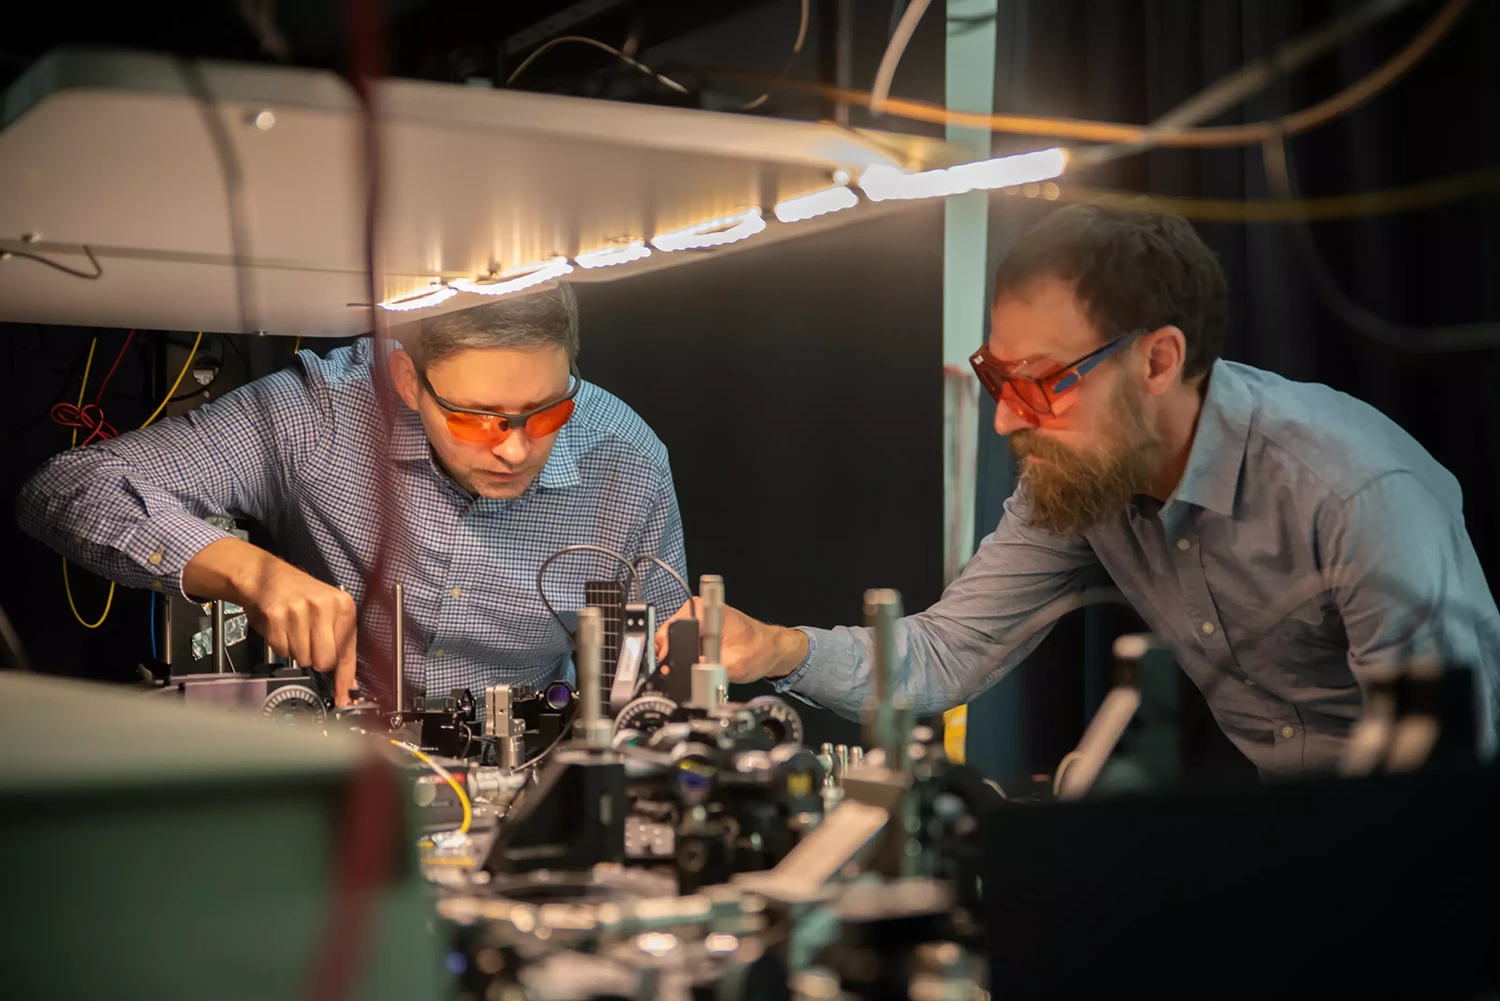
NIST researchers demonstrated a quantum position verification protocol that could prevent unauthorized access by confirming physical location.
Threat ResearchIncident1d ago · 1 source
Rapid7 launched its Threat Intelligence Hub to enhance threat response for security teams.
RansomwareIncident1d ago · 1 source
Ransomware and extortion gangs claimed about 718 victims a month through October 2026, according to threat intelligence firm ZeroFox, up from roughly 573 a month in 2025.
Cloud & IdentityIncident1d ago · 1 source
Six critical vulnerabilities in F5 BIG-IP allow an attacker to crash the Traffic Management Microkernel (TMM) without logging in, disrupting traffic until the TMM restarts.
VulnerabilitiesIncident1d ago · 1 source
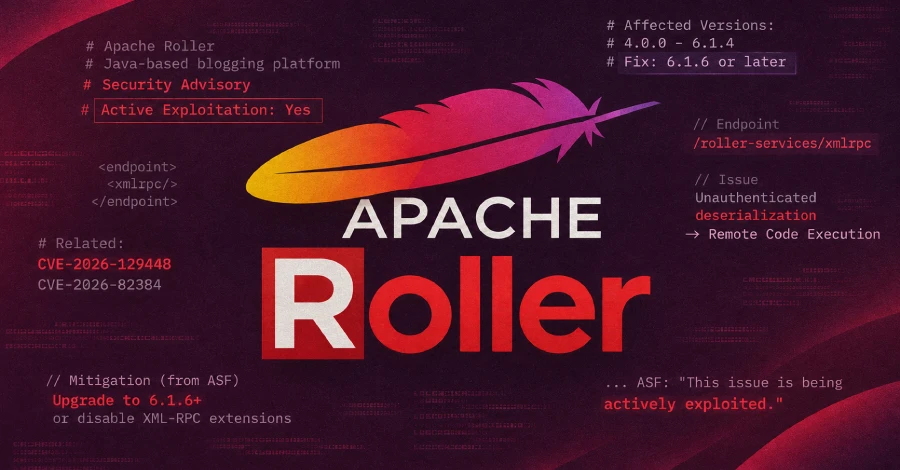
A critical vulnerability in Apache Roller allows unauthenticated remote code execution, with active exploitation reported.
VulnerabilitiesIncident1d ago · 1 source
A newly disclosed security flaw in Windows Hello warrants attention from all users.
VulnerabilitiesIncident1d ago · 1 source
Optimizely's vulnerability allowed malware to target users of major websites, highlighting risks in third-party JavaScript dependencies.
Cyber AttacksIncident2d ago · 1 source
A new Linux-based cryptomining malware, SANSAR, uses modified NVIDIA libraries to conceal GPU activity, raising concerns for organizations utilizing GPU resources.
AI SecurityIncident2d ago · 1 source
AI pentesting is gaining traction as organizations seek to address security gaps in rapid software development cycles.
Cyber Attacks2d ago · 1 source
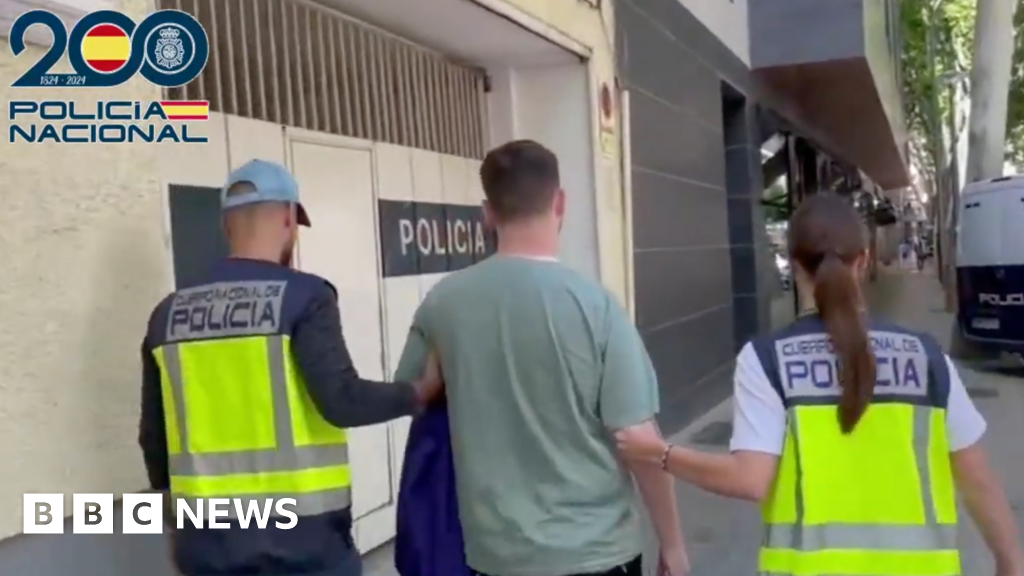
A British hacker received a six-year prison sentence in the U.S. for stealing over $11 million through SMS phishing schemes targeting cryptocurrency investors.
AI SecurityIncident2d ago · 1 source
Canonical allows Ubuntu Pro users to test AI-generated security patches early through the Edge archive.