Bitter Hackers Deploy New PapRAT Backdoor in Cyberespionage Campaign Targeting South Asia
The Bitter cyber espionage group is using a new backdoor called PapRAT to target South Asian organizations, Fortinet researchers found.
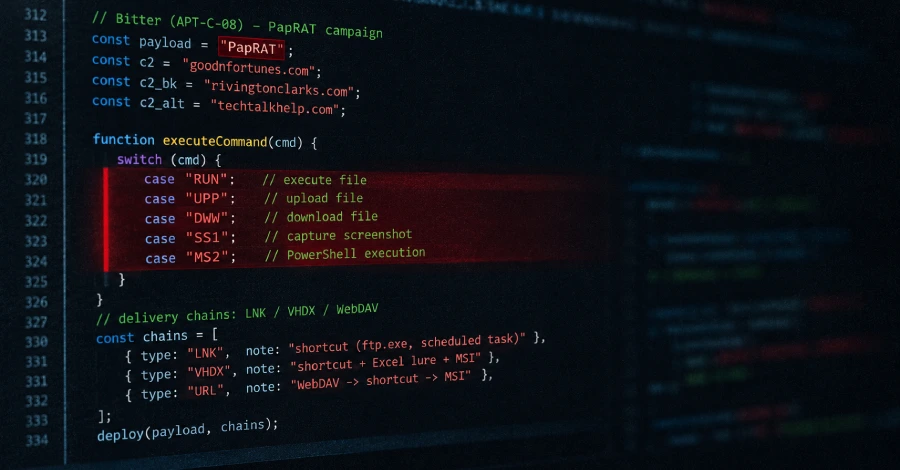
The Bitter group, a South Asian cyber espionage entity, has been identified using a new remote access trojan named PapRAT in attacks on organizations in South Asia. This development was revealed by Fortinet FortiGuard Labs, which noted the malware's capabilities and the complexity of the attack chains involved. The campaign is significant due to its use of multiple infection methods and the advanced functionalities of PapRAT, which is implemented in both C++ and Rust.
PapRAT is designed to perform various malicious activities, including executing commands, uploading and downloading files, deleting files, and capturing screenshots. The Rust implementation of PapRAT further extends its capabilities by adding PowerShell execution and other command functionalities. The attack leverages three distinct infection chains, with a notable focus on living-off-the-land techniques that execute commands from a remote server, allowing the attackers to gather extensive reconnaissance data from the targeted systems.
The first infection chain utilizes a server named "goodnfortunes[.]com" to collect information such as directory and task lists, antivirus product data, and mounted drives. This data is then exfiltrated to the command-and-control server using a curl command. A second variant of the attack retrieves a file from "techtalkhelp[.]com," which contains a script for further instructions executed as PowerShell commands. This method provides operational flexibility by allowing command updates without deploying new binaries, making detection more challenging.
The third attack chain combines elements of the first two, using a script to download an MSI installer via curl. This installer acts as a conduit for PapRAT and subsequently deploys WmRAT, another malware linked to Bitter.
What security teams should do
Monitor for malicious behavior involving scripting tools, scheduled tasks, and installer activity.
What remains unknown
The specific organizations targeted by the Bitter group in this campaign are not identified.
The full extent of the impact on the affected organizations is not detailed.