Hackers Hijack Five OVHcloud CLI Releases to Distribute Secret-Stealing Malware
An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19.
OVHcloud CEO Octave Klaba disclosed that the company’s CLI repository on GitHub had been compromised, urging users who downloaded the latest version yesterday to update or remove the tool.
French cloud and hosting provider OVHcloud is warning users that attackers compromised its open-source command-line interface (CLI) tool to distribute information-stealing malware.
If you are affected, please change all the secrets on your disk." According to OpenSourceMalware, a community-driven threat intelligence platform, the attack was likely part of a new GlassWorm operation, known for campaigns since late 2025 that impacted the VSCode , OpenVSX , GitHub, and npm software development ecosystems.
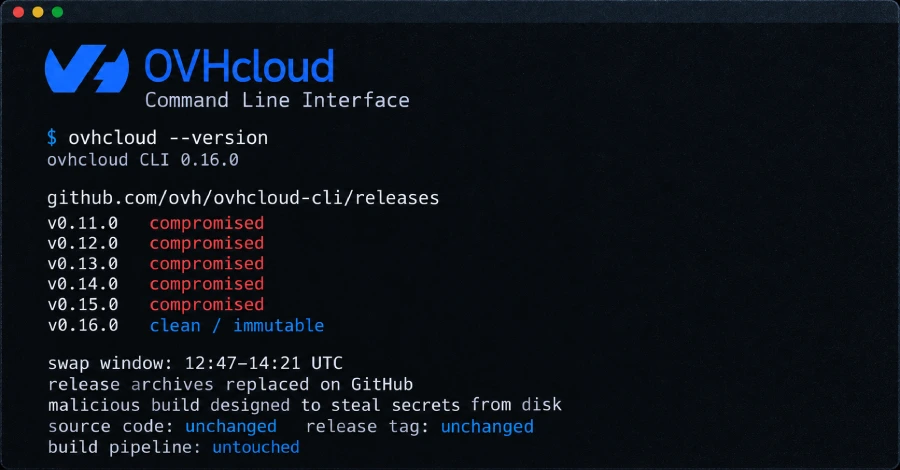
They were live on GitHub for up to 94 minutes, from 12:47 to 14:21 UTC, and reached only people who installed or updated the OVHcloud CLI during that window, via a path that checks for no hash, on macOS, Linux x86_64 or arm64, or Windows x86_64.
An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19.
The researchers note that the GitHub account used in the attack had been compromised for more than half a year.
The account had been hijacked, and the new files were a build designed to steal secrets stored on the disk of any machine that runs it, the cloud provider says.
In a second post on Monday night, quoted by Next , Klaba wrote that the problem stemmed from the immutability option not being activated, so a user with the right permissions could modify existing releases directly on GitHub without any checks by the company's CI/CD pipeline.
The researchers confirmed that the attacker did not tamper with the CI/CD pipelines and uploaded malware-infected packages built locally.
OVHcloud deleted the swapped archives and published a clean v0.16.0 that evening as an immutable release, whose files GitHub will not let anyone change.
What happened
OVHcloud CEO Octave Klaba disclosed that the company’s CLI repository on GitHub had been compromised, urging users who downloaded the latest version yesterday to update or remove the tool.
French cloud and hosting provider OVHcloud is warning users that attackers compromised its open-source command-line interface (CLI) tool to distribute information-stealing malware.
What changed
If you are affected, please change all the secrets on your disk." According to OpenSourceMalware, a community-driven threat intelligence platform, the attack was likely part of a new GlassWorm operation, known for campaigns since late 2025 that impacted the VSCode , OpenVSX , GitHub, and npm software development ecosystems.
They were live on GitHub for up to 94 minutes, from 12:47 to 14:21 UTC, and reached only people who installed or updated the OVHcloud CLI during that window, via a path that checks for no hash, on macOS, Linux x86_64 or arm64, or Windows x86_64.
Who is affected
An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19.
The researchers note that the GitHub account used in the attack had been compromised for more than half a year.
Why it matters
The account had been hijacked, and the new files were a build designed to steal secrets stored on the disk of any machine that runs it, the cloud provider says.
In a second post on Monday night, quoted by Next , Klaba wrote that the problem stemmed from the immutability option not being activated, so a user with the right permissions could modify existing releases directly on GitHub without any checks by the company's CI/CD pipeline.
Technical details
The researchers confirmed that the attacker did not tamper with the CI/CD pipelines and uploaded malware-infected packages built locally.
OVHcloud deleted the swapped archives and published a clean v0.16.0 that evening as an immutable release, whose files GitHub will not let anyone change.
You got a swapped file if, in that window and on one of those platforms, you: The customer who caught the swap pulled the build information out of the new v0.15.0 Linux arm64 binary with go version -m, which reads the file without running it, and posted it in a GitHub issue .
Response
The source code, the release tag, and the company's build pipeline were not touched: the bad build was a plain go build of a later commit, uploaded straight onto releases published between April and September.
In a later update, Klaba shared that GitHub’s release immutability setting was disabled, allowing a sufficiently privileged account to modify existing releases without passing CI/CD checks.
What security teams should do
Those five releases were published between April 14 and September 16, so a copy installed before 12:47 UTC on Monday and not updated since is the original.
Klaba said that the compromised release appeared at 14:47 on October 19 and was detected and blocked at 16:21 after a customer reported it.
Attribution
The Hacker News: An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19.
BleepingComputer: French cloud and hosting provider OVHcloud is warning users that attackers compromised its open-source command-line interface (CLI) tool to distribute information-stealing malware.
What to watch next
Watch for updated vendor guidance and fixed-version details.