WinRAR Gorbag Hackers Exploit WinRAR Flaw to Deploy Data-Stealing Malware
WinRAR has a newly disclosed security flaw that anyone running it should know about.
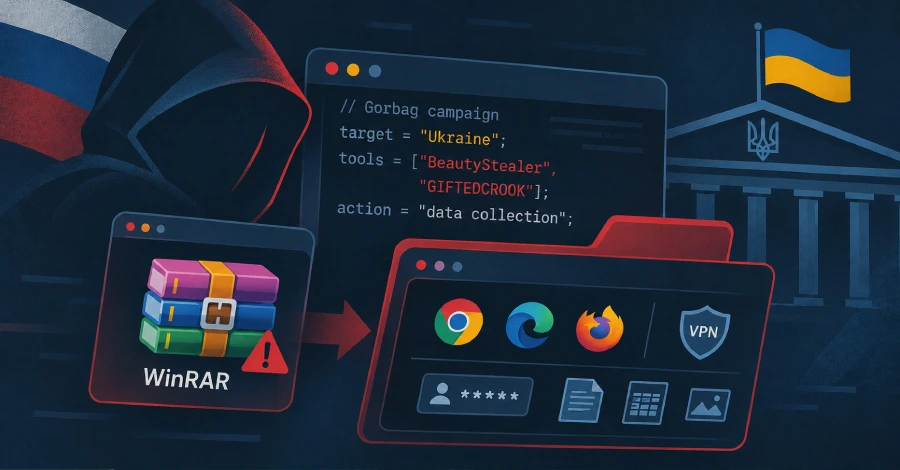
A Russia-aligned threat actor known as Gorbag has been observed using simple information stealer malware in attacks targeting Ukrainian organizations.
In early 2026, the group switched to RAR archives exploiting CVE-2025-8088 , a WinRAR path traversal flaw ESET reported in August 2025 after seeing RomCom, another Russia-aligned group, exploit it as a zero-day.
Earlier this June, Trend Micro also attributed the adversary to attacks weaponizing a now-patched vulnerability in WinRAR (CVE-2025-8088) to trigger a DLL sideloading chain responsible for executing GIFTEDCROOK.
Gorbag is known to be active since at least February 2025.
The collected data is compressed into an archive and sent to an attacker-controlled Telegram chat or a custom command-and-control (C2) server that implements FastAPI.
Initial attack waves observed in early 2025 have utilized Prime ReverseShell, a derivative of PSSW100AVB that functions as a reverse shell to execute commands on compromised systems and return the results back to a C2 server.
Stealer malware deployed by Gorbag is also equipped to harvest VPN configurations and documents of interest, raising the possibility that it may be acting as an initial access broker that hands off stolen data to other threat actors, who then can conduct post-exploitation activity of their own.
BeautyStealer is the primary data-harvesting tool that can capture data from Chrome, Edge, Opera, and Firefox, OpenVPN configurations, and files matching specific extensions, including Microsoft Office documents, archives, emails, KeePass databases, remote desktop protocol (RDP) configurations, and VPN configurations.
Schaeffer told DKCISSP via email that BeautyStealer is an evolution of the GIFTEDCROOK malware with common roots, adding Gorbag has completely shifted to using only the BeautyStealer variant since the end of December 2025.
The cybersecurity company has also confirmed that the CVE-2025-8088 compromise chain documented by Trend Micro actually leads to the deployment of a BeautyStealer variant.
What happened
A Russia-aligned threat actor known as Gorbag has been observed deploying simple information-stealer malware in attacks against Ukrainian organizations.
In early 2026, the group began utilizing RAR archives to exploit CVE-2025-8088, a WinRAR path traversal flaw that ESET reported in August 2025, following its use as a zero-day by RomCom, another Russia-aligned group.
What changed
Earlier this June, Trend Micro attributed the adversary to attacks that weaponized a now-patched vulnerability in WinRAR (CVE-2025-8088), triggering a DLL sideloading chain responsible for executing GIFTEDCROOK.
Gorbag has been active since at least February 2025.
Who is affected
The stolen data is compressed into an archive and sent to an attacker-controlled Telegram chat or a custom command-and-control (C2) server that utilizes FastAPI.
Initial attack waves observed in early 2025 employed Prime ReverseShell, a derivative of PSSW100AVB, which functions as a reverse shell to execute commands on compromised systems and send the results back to a C2 server.
Why it matters
The stealer malware deployed by Gorbag is capable of harvesting VPN configurations and documents of interest, indicating it may act as an initial access broker that hands off stolen data to other threat actors for subsequent post-exploitation activities.
BeautyStealer is the primary data-harvesting tool, capable of capturing data from Chrome, Edge, Opera, and Firefox, as well as OpenVPN configurations and files with specific extensions, including Microsoft Office documents, archives, emails, KeePass databases, remote desktop protocol (RDP) configurations, and VPN configurations.
Technical details
Schaeffer informed DKCISSP via email that BeautyStealer is an evolution of the GIFTEDCROOK malware, sharing common roots, and noted that Gorbag has entirely shifted to using only the BeautyStealer variant since late December 2025.
The cybersecurity company has confirmed that the compromise chain for CVE-2025-8088, documented by Trend Micro, leads to the deployment of a BeautyStealer variant.
In one instance, a macro-enabled Excel spreadsheet (.XLSM) serves as a conduit to run a VBA payload, which subsequently decodes and executes BeautyStealer.
Response
It is not malicious; the program simply performs prime number generation from 1 to 900, attempting to deceive AI assistants and security products reviewing the file," ESET stated.
Attribution
The Hacker News: A Russia-aligned threat actor known as Gorbag has been observed using simple information stealer malware in attacks targeting Ukrainian organizations.
Infosecurity Magazine: Damien Schaeffer of ESET detailed the group, which the firm named Gorbag, in research published on November 3, after presenting it at Virus Bulletin in October.
What to watch next
Watch for new exploitation reports and updated indicators of compromise.
Watch for updated vendor guidance and fixed-version details.