Six Unpatched Danfoss Refrigeration Controller Flaws Could Allow Remote Takeover Without Login
Security researchers have identified six unpatched vulnerabilities in Danfoss AK-SM800A refrigeration controllers that could allow remote takeover without authentication.
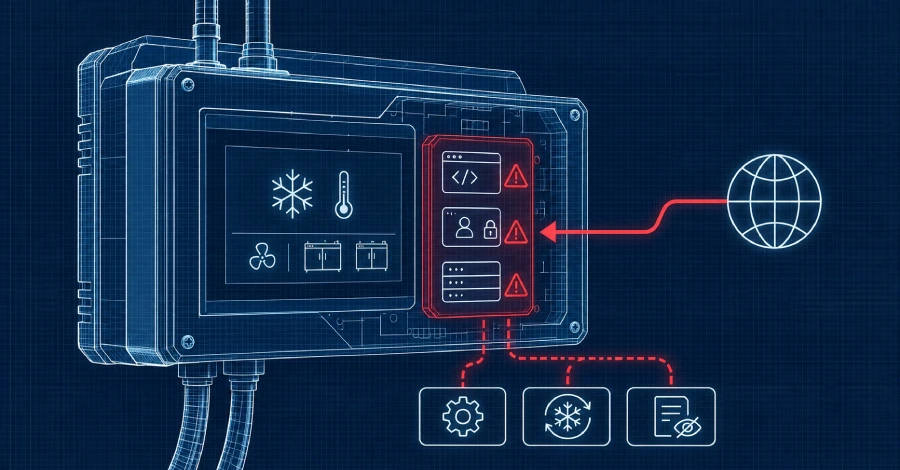
Six vulnerabilities in Danfoss AK-SM800A refrigeration controllers could enable remote attackers to take control of the devices without needing to log in, according to findings from Dutch security consultancy Midnight Blue. This situation is concerning as no patches are currently available to address these issues.
The identified flaws are particularly alarming because they affect the controllers used to manage refrigeration systems in commercial settings. The vulnerabilities could potentially allow unauthorized users to manipulate the settings of the controllers, which could lead to operational disruptions and financial losses. The researchers noted that the latest firmware release, version 5.4.0, does not resolve these security issues, leaving systems exposed.
In response to the findings, cybersecurity agencies in Belgium, Ireland, and Germany have advised operators to remove the management interfaces of these controllers from internet exposure. They emphasized that simply updating firmware, changing default passwords, or enabling Strict mode is insufficient to secure the devices. Strict mode is designed to enhance security by requiring encrypted connections and session tokens, but one of the flaws resides within the gateway that enforces this protection.
The AK-SM800A controllers are critical for managing refrigeration units in various commercial environments. They allow maintenance firms to oversee operations remotely. However, the potential for exploitation is heightened, as evidenced by recent attacks across Europe that began in October, which led to unwanted defrost cycles and significant product losses. Although the German federal IT security agency acknowledged previous incidents involving these controllers, it has not confirmed any exploitation of the newly identified vulnerabilities.
The vulnerabilities were uncovered during a manual review by Midnight Blue's Carlo Meijer, who found that five of the flaws exist in web request handlers that do not require authentication. This means that attackers could leverage these weaknesses to execute code with root privileges on affected devices. The sixth flaw is particularly concerning as it resides in the gateway enforcing Strict mode, which could be manipulated to allow unauthorized access.
The researchers have advised that removing internet exposure should be prioritized over waiting for a patch, as the vulnerabilities could be exploited at any time. The Belgian and Irish agencies echoed this sentiment, recommending that operators should ensure their controllers are not directly accessible from the public internet. Additionally, they suggested that anyone suspecting a compromise should change all credentials and verify that any connected equipment is functioning correctly.
What security teams should do
- Remove the management interfaces of the AK-SM800A controllers from internet exposure.
- Change all default passwords and ensure that Strict mode is enabled.
- Verify the functionality of all equipment connected to the controllers.
- Monitor for any signs of compromise in the controller systems.
What it meansThese vulnerabilities highlight a significant risk for operational technology systems, particularly those exposed to the internet.
Ask IT this weekAre our Danfoss AK-SM800A controllers exposed to the internet?Have we implemented all recommended security measures for our refrigeration systems?
DecisionEnsure that all controllers are not directly accessible from the public internet.