CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands
Fraudulent reward portals and fake gift card giveaways are surging globally, tricking users into deceptive verification loops and paid subscriptions.
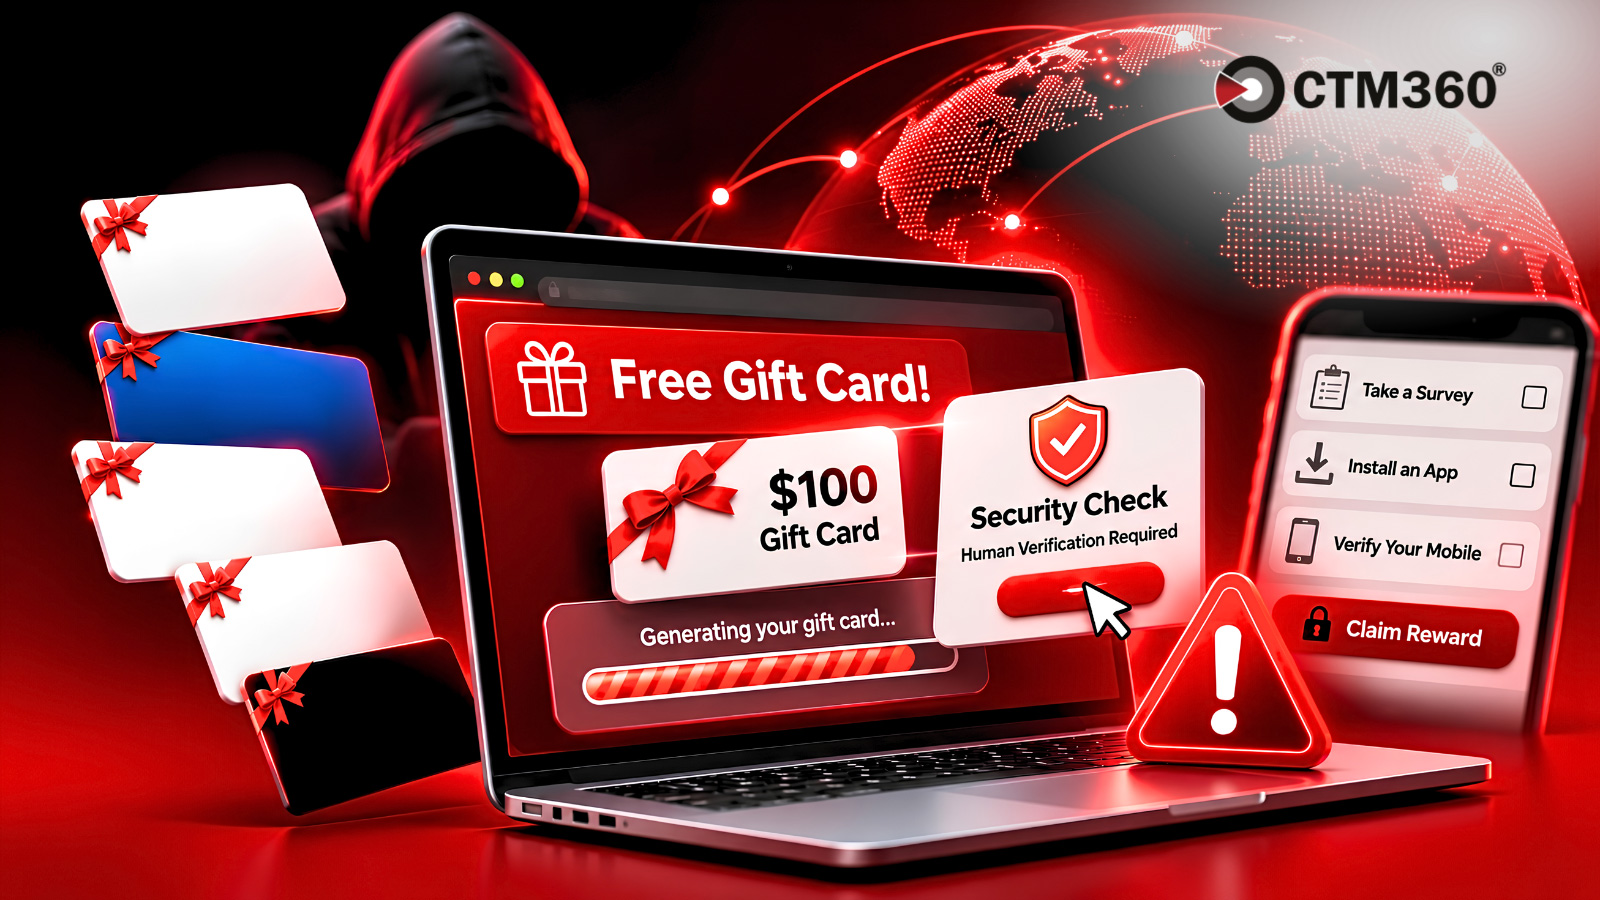
Fraudulent reward portals and fake gift card giveaways are surging globally, tricking users into deceptive verification loops and paid subscriptions.
These scams lure victims with a simple pitch: click an ad featuring a celebrity endorsement, claim a free gift card from a well-known brand, and complete a quick human verification step to unlock the reward.
Read the full report here: https://www.ctm360.com/reports/gift-card-scams Behind the polished branding, fake progress bars, and convincing promotional messages, however, no actual gift cards are provided.
Instead, these campaigns operate as large-scale affiliate monetization schemes designed to collect personal information, generate application installs, and enroll unsuspecting users in recurring mobile subscriptions.
Based on activity observed by CTM360, analysts identified more than 1,000 incidents linked to this recurring campaign.
To increase credibility and attract potential victims, the campaigns rely heavily on social media distribution through: Because the underlying infrastructure is highly modular, threat actors can swap out the impersonated brand, celebrity lure, and domain name without rebuilding the core scam engine.
CTM360 maps this activity using a structured fraud lifecycle, highlighting how victims are systematically pushed through a psychological progression of curiosity, trust, and urgency.
Once a user clicks a malicious ad, they are redirected to a fraudulent reward portal.
After a victim selects a gift card value, the site runs a scripted, visual progress animation simulating the generation of the card on the back end.
Before the full code is revealed, the victim is presented with a deceptive Security Check or Human Verification gate.
Threat actors exploit consumer familiarity with established brands, frequently impersonating major retailers and consumer platforms such as PlayStation, Sephora, SHEIN, Walmart, and Amazon.
Discover how threat actors use brand impersonation and fake rewards to exploit users.
The human verification step is a deceptive pivot into what CTM360 identifies as Rather than performing a legitimate security check, the verification process redirects victims to third-party activities designed to generate revenue for the operators.
Detect Cyber Threats 24/7 with CTM360: Monitor, analyze, and promptly mitigate risks across your external digital landscape with the CTM360.
What happened
Fraudulent reward portals and fake gift card giveaways are surging globally, tricking users into deceptive verification loops and paid subscriptions.
These scams lure victims with a simple pitch: click an ad featuring a celebrity endorsement, claim a free gift card from a well-known brand, and complete a quick human verification step to unlock the reward.
Read the full report here: https://www.ctm360.com/reports/gift-card-scams Behind the polished branding, fake progress bars, and convincing promotional messages, however, no actual gift cards are provided.
What changed
Instead, these campaigns operate as large-scale affiliate monetization schemes designed to collect personal information, generate application installs, and enroll unsuspecting users in recurring mobile subscriptions.
Based on activity observed by CTM360, analysts identified more than 1,000 incidents linked to this recurring campaign.
To increase credibility and attract potential victims, the campaigns rely heavily on social media distribution through: Because the underlying infrastructure is highly modular, threat actors can swap out the impersonated brand, celebrity lure, and domain name without rebuilding the core scam engine.
Who is affected
CTM360 maps this activity using a structured fraud lifecycle, highlighting how victims are systematically pushed through a psychological progression of curiosity, trust, and urgency.
Once a user clicks a malicious ad, they are redirected to a fraudulent reward portal.
Why it matters
After a victim selects a gift card value, the site runs a scripted, visual progress animation simulating the generation of the card on the back end.
Before the full code is revealed, the victim is presented with a deceptive Security Check or Human Verification gate.
Technical details
Threat actors exploit consumer familiarity with established brands, frequently impersonating major retailers and consumer platforms such as PlayStation, Sephora, SHEIN, Walmart, and Amazon.
Discover how threat actors use brand impersonation and fake rewards to exploit users.
Response
The human verification step is a deceptive pivot into what CTM360 identifies as Rather than performing a legitimate security check, the verification process redirects victims to third-party activities designed to generate revenue for the operators.
Detect Cyber Threats 24/7 with CTM360: Monitor, analyze, and promptly mitigate risks across your external digital landscape with the CTM360.
Attribution
BleepingComputer: Fraudulent reward portals and fake gift card giveaways are surging globally, tricking users into deceptive verification loops and paid subscriptions.
What to watch next
Watch for additional victim details, indicators of compromise and follow-on exploitation reports.