Researchers Detail iPhone Flaw That Let Apps Record Audio Despite Denied Microphone Permission
A now-patched flaw in Apple's audio service let apps on iPhones and iPads record audio even after the user tapped Don't Allow on the microphone prompt.
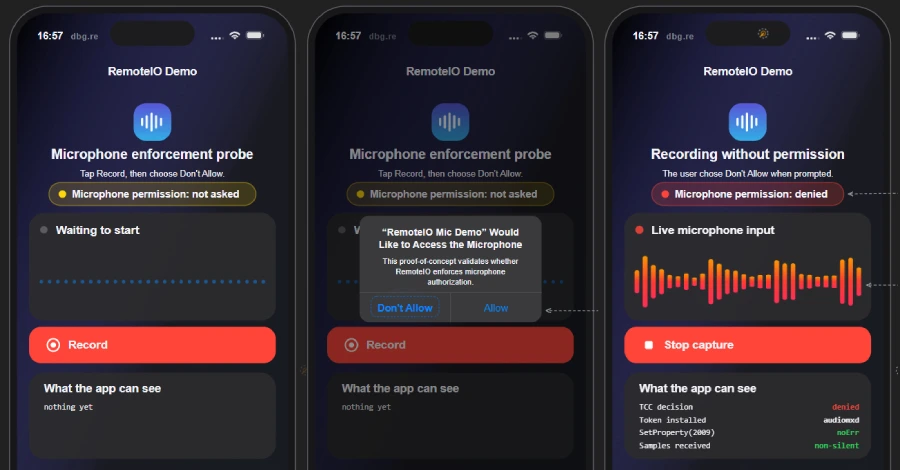
A now-patched flaw in Apple's audio service let apps on iPhones and iPads record audio even after the user tapped Don't Allow on the microphone prompt.
The first security updates with the fix came out on August 17; neither Apple nor the two researchers who found the flaw report that it was used in attacks.
Mustafa Calap, a security engineer who reported the same flaw separately, published his own analysis the same day; calap reproduced the bypass on iOS 26.6, released July 27, and on an iPadOS 27 beta.
In the earlier build of his technical analysis, the system logs showed no record of the app using the microphone; neither researcher describes a way for users to check whether an app recorded them before the fix.
His demo video shows the indicator while the test app records with no microphone permission, and calap's test app recorded while its permission still read denied, according to his detailed write-up.
His two test apps were sandboxed apps with no added entitlements.
Both apps were installed from Xcode and never went through App Review; so the tests do not show whether App Review would have stopped such an app.
Why it matters
An app could send the service a token that named audiomxd itself; it took a shortcut meant for its own internal audio and allowed recording without asking TCC.