British hacker who stole $11m jailed for six years in US
A British hacker received a six-year prison sentence in the U.S. for stealing over $11 million through SMS phishing schemes targeting cryptocurrency investors.
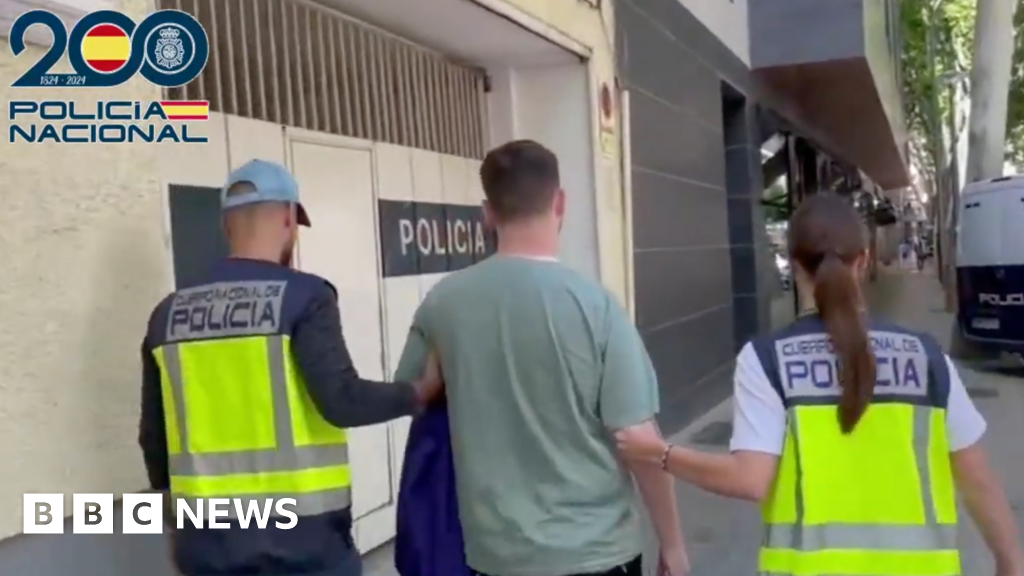
Tyler Buchanan, a 24-year-old from Dundee, has been sentenced to six years in a federal prison in the United States for his role in a hacking campaign that targeted at least a dozen companies through text message phishing, resulting in the theft of more than $11.6 million in cryptocurrency from individual victims.
Buchanan was part of the hacker collective known as Scattered Spider, which has been linked to a series of high-profile cybercrimes. U.S. prosecutors described the consequences of the thefts as severe and life-altering for victims, underscoring the growing threat posed by online crime groups. The sentencing concludes a lengthy international investigation involving law enforcement from the UK, U.S., Spain, and Canada.
The hacking campaign, which began in 2021 when Buchanan was just 19 years old, involved him and other English-speaking hackers targeting employees at major technology and telecommunications companies. Operating from his parents' home, Buchanan and his associates sent out hundreds of SMS messages to mobile phones of employees, luring them to spoof websites designed to mimic legitimate company sites.
SMS phishing, also known as smishing, is a type of cyber attack where attackers send fraudulent text messages to trick recipients into revealing sensitive information. These messages often contain links to fake websites that resemble legitimate ones, prompting users to enter personal information such as usernames and passwords. Attackers can then use this data for identity theft or financial fraud.
Buchanan's group used these phishing techniques on an industrial scale, setting up a Telegram bot to collect the credentials of unsuspecting victims. The stolen information included confidential work details, intellectual property, and personal identifying information. Following the initial thefts, the group employed SIM-swapping techniques to target cryptocurrency investors in the U.S., leading to significant financial losses.
One notable incident involved a victim losing $1.67 million in December 2022, which was part of the overall theft totaling over $11.6 million. Additionally, Buchanan's online identity was exposed by rival hackers in early 2023, leading to threats and violence against him, prompting him to flee to Canada before returning to the UK.
In April 2023, Police Scotland, acting on a request from the FBI, searched Buchanan's home and uncovered a device containing sensitive information about hacking victims, including cryptocurrency seed phrases. He was arrested on May 31, 2024, at Palma de Mallorca Airport in Spain while attempting to board a flight to Naples. After being extradited to the U.S., he remained in custody before his sentencing this week.
Buchanan was charged alongside four American associates linked to Scattered Spider, which has been implicated in various cyber attacks. Two other members of the group were previously sentenced in the UK for their involvement in attacks that caused significant financial damage, including a disruptive attack against Transport for London.
It is unclear how many total victims were affected by Buchanan's phishing campaign.
The extent of the financial impact on victims beyond the reported $11.6 million is not fully known.
Details on the full scope of Scattered Spider's operations and the identities of all its members remain undisclosed.
What it meansA hacker was sentenced for stealing over $11 million through SMS phishing, highlighting the risks of social engineering attacks targeting employees.
Ask your IT team this weekWhat measures do we have in place to train employees against phishing attacks?How are we monitoring for unauthorized access to sensitive information?
DecisionThe IT team will review and enhance employee training on phishing awareness, with security verifying its implementation.