Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.
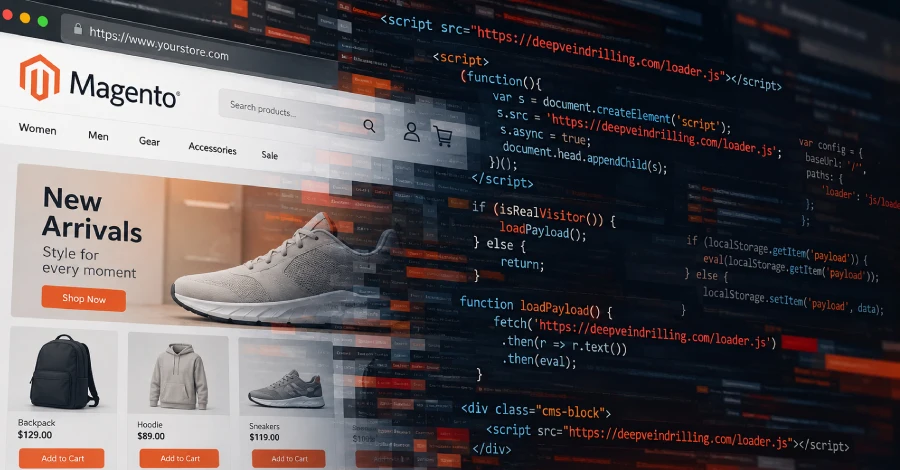
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.
In a follow-up analysis, Nokia Deepfield researchers described the malware as a Mirai fork which uses "ChaCha20 for the static config table (the first time we have seen ChaCha20 used this way in a Mirai variant), a single static byte (0xED) for everything on the wire, a named reverse-shell protocol (SHELL / SHOUT) on the same channel as attack commands, and a DNS misdirection scheme that swaps the two 16-bit halves of every resolved A record before connect()." Arctic Wolf, which also shared further details of the same weaponized PHP2Shell exploitation attempt, said the botnet supports 24 commands to enable flood attacks over ICMP, TCP, UDP, and OpenVPN protocol.
On Friday, the PHP security team also shared mitigation measures for a new RCE vulnerability (tracked as CVE-2026-115560) that has no patch and can only be exploited when targeting systems "with an unusual combination of configuration and application code." Until a security patch is released, the PHP devs advised admins to set session.upload_progress.enabled=0 to block potential attacks, a mitigation already recommended before patches for the PHP2Shell security updates were released.
The disclosure comes against the backdrop of PHP2Shell , a set of two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) that have witnessed widespread exploitation attempts following their disclosure last week.
According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store's pages that, when visited by unsuspecting users, serves malicious JavaScript loader code through Magento CMS blocks.
Only updating PHP on the host itself closes the gap." Perplexity researcher Adel Karimi has recorded what appears to be the first in-the-wild (ITW) successful exploitation of the PHP2Shell vulnerabilities to run shell commands on honeypot servers.
Web infrastructure company Cloudflare said it observed tens of thousands of attempts to exploit the flaw 45 minutes after the flaws were publicly announced, before climbing to hundreds of thousands within 2 hours and millions as of early October 22, 2026.
None was exploited." The disclosure also coincides with the development of a PHP2Shell exploit that can achieve remote code execution on ASLR-enabled x86-64 systems with PHP's recommended production configuration.
In an update, Palo Alto Networks Unit 42 said it's retracting its earlier assessment that the post-compromise activity targeting the European government agency involved the exploitation of the PHP2Shell flaws.
Two critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619), collectively tracked as PHP2Shell, have been successfully exploited in the wild.
What happened
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.
In a follow-up analysis, Nokia Deepfield researchers described the malware as a Mirai fork which uses "ChaCha20 for the static config table (the first time we have seen ChaCha20 used this way in a Mirai variant), a single static byte (0xED) for everything on the wire, a named reverse-shell protocol (SHELL / SHOUT) on the same channel as attack commands, and a DNS misdirection scheme that swaps the two 16-bit halves of every resolved A record before connect()." Arctic Wolf, which also shared further details of the same weaponized PHP2Shell exploitation attempt, said the botnet supports 24 commands to enable flood attacks over ICMP, TCP, UDP, and OpenVPN protocol.
What changed
On Friday, the PHP security team also shared mitigation measures for a new RCE vulnerability (tracked as CVE-2026-115560) that has no patch and can only be exploited when targeting systems "with an unusual combination of configuration and application code." Until a security patch is released, the PHP devs advised admins to set session.upload_progress.enabled=0 to block potential attacks, a mitigation already recommended before patches for the PHP2Shell security updates were released.
The disclosure comes against the backdrop of PHP2Shell , a set of two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) that have witnessed widespread exploitation attempts following their disclosure last week.
Who is affected
According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store's pages that, when visited by unsuspecting users, serves malicious JavaScript loader code through Magento CMS blocks.
Only updating PHP on the host itself closes the gap." Perplexity researcher Adel Karimi has recorded what appears to be the first in-the-wild (ITW) successful exploitation of the PHP2Shell vulnerabilities to run shell commands on honeypot servers.
Why it matters
Web infrastructure company Cloudflare said it observed tens of thousands of attempts to exploit the flaw 45 minutes after the flaws were publicly announced, before climbing to hundreds of thousands within 2 hours and millions as of early October 22, 2026.
None was exploited." The disclosure also coincides with the development of a PHP2Shell exploit that can achieve remote code execution on ASLR-enabled x86-64 systems with PHP's recommended production configuration.
Technical details
In an update, Palo Alto Networks Unit 42 said it's retracting its earlier assessment that the post-compromise activity targeting the European government agency involved the exploitation of the PHP2Shell flaws.
Two critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619), collectively tracked as PHP2Shell, have been successfully exploited in the wild.
Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant called Potassium , as it emerges that weaponizing the flaws may be harder than previously thought.
Response
The scripts, according to the cybersecurity company, checked about 20 public websites for the PHP version, server setup, and session settings the exploit needs.
The ultimate objective of the attack is to launch the attack-controlled code when the CMS block is rendered after a shopper opens the compromised website.
What security teams should do
PHP2Shell Flaws Puts Organizations on Alert — The PHP Foundation released patches for two critical vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619, that could lead to unauthenticated remote code execution.
While details on the PHP2Shell security flaws (including the CVE IDs and mitigation advice provided to some critical infrastructure providers) leaked online and some proof-of-concept (PoC) exploits were published before the patches went live, the PHP security team said that none were functional.
What remains unknown
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.
Attribution
The Hacker News: An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.
The Hacker News: In an update, Palo Alto Networks Unit 42 said it's retracting its earlier assessment that the post-compromise activity targeting the European government agency involved the exploitation of the PHP2Shell flaws.
The Hacker News: Critical bugs that let attackers run code remotely are showing up everywhere.
BleepingComputer: Two critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619), collectively tracked as PHP2Shell, have been successfully exploited in the wild.
What to watch next
Watch for new exploitation reports and updated indicators of compromise.
Watch for updated vendor guidance and fixed-version details.