Hackers Hide Linux Backdoor in Control Web Panel Server to Execute Commands Without Logs
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at QiAnXin's XLab said this week.
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at QiAnXin's XLab said this week.
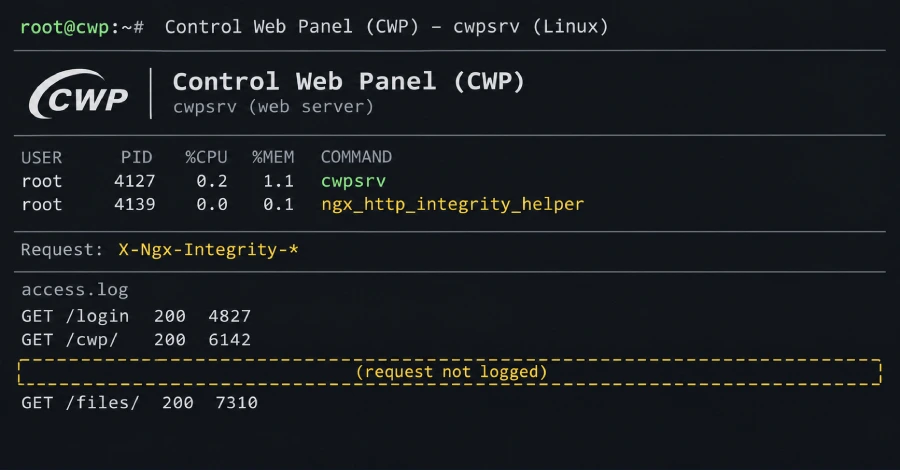
The backdoored web server executes commands that attackers send via web requests, and those requests never appear in its access logs; installing it takes root access, so the attackers must already control the server.
The backdoor is cwpsrv itself, rebuilt with extra code, the researchers found in their technical analysis , and in the researchers' example, the socket check found the backdoor on a server where the list of open ports looked normal.
The archive uploaded from Brazil also held the Ebury malware , an OpenSSH backdoor and credential stealer active since at least 2009.
The researchers, who named the backdoor cwpdoor , captured its installer, a shell script posing as a version update, on June 29; the installer handles only two versions of that web server, cwpsrv 1.15.10 and 1.24.0.
The researchers do not yet know how attackers get the root access the installer needs.
On September 30, an archive holding a copy of the backdoor was uploaded to VirusTotal from Brazil.
When the installer replaces the cwpsrv file, it puts the file's dates back to their original values, so checks with ls and stat show it as unchanged.
When the researchers checked, the backdoor file had zero detections out of 63 on VirusTotal.
What happened
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at QiAnXin's XLab said this week.
The backdoored web server executes commands that attackers send via web requests, and those requests never appear in its access logs; installing it takes root access, so the attackers must already control the server.
What changed
The backdoor is cwpsrv itself, rebuilt with extra code, the researchers found in their technical analysis , and in the researchers' example, the socket check found the backdoor on a server where the list of open ports looked normal.
The archive uploaded from Brazil also held the Ebury malware , an OpenSSH backdoor and credential stealer active since at least 2009.
Who is affected
The researchers, who named the backdoor cwpdoor , captured its installer, a shell script posing as a version update, on June 29; the installer handles only two versions of that web server, cwpsrv 1.15.10 and 1.24.0.
Why it matters
The researchers do not yet know how attackers get the root access the installer needs.
Technical details
On September 30, an archive holding a copy of the backdoor was uploaded to VirusTotal from Brazil.
When the installer replaces the cwpsrv file, it puts the file's dates back to their original values, so checks with ls and stat show it as unchanged.
Response
When the researchers checked, the backdoor file had zero detections out of 63 on VirusTotal.
Attribution
The Hacker News: A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for managing Linux hosting servers, researchers at QiAnXin's XLab said this week.
What to watch next
Watch for additional victim details, indicators of compromise and follow-on exploitation reports.
Watch for revised vendor guidance, fixed versions and mitigation updates.