Binance Reveals How Fake Job Interviews and AI Tool Abuse Led to $6.43 Billion Theft
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a sophisticated, multi-stage campaign that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
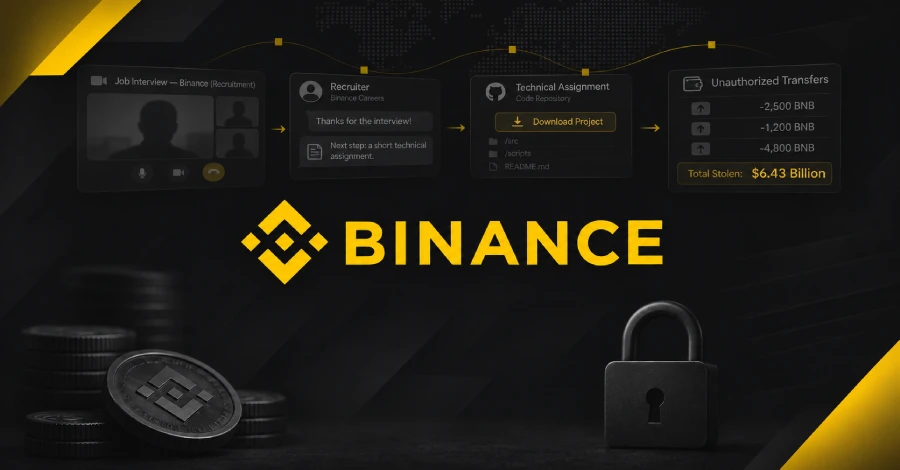
Although Binance said it detected the attack and rotated all related credentials as a precautionary step, the company said information about "Engineer A's role and his related colleagues on our wallet infrastructure team was exposed to the hacker." The second part of the attack occurred in September 2026, with the threat actor contacting another engineer (named "Engineer B") via a legitimate job-hunting platform by disguising themselves as a Project Director.
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
BTCPay Server, a self-hosted, open-source cryptocurrency payment processor, has urged users to install the latest version of its software in response to reports of Bitcoin and Litecoin being stolen from hot wallets on instances running older versions.
Initial findings published by the company, which operates the world's largest cryptocurrency exchange, said hackers gained access to its systems through "sophisticated, multi-stage campaign".
Systems touched in the attack path have been rebuilt or replaced," Binance said.
These see hackers use approaches such as phishing to trick people into parting with sensitive or personal details, that can then be used to try and access their accounts.
But on Tuesday, the company wrote in its post on X : "The latest information released by the Federal Bureau of Investigation indicates that the Democratic People's Republic of Korea is responsible for this incident." As part of its security efforts following the attack, Binance said it would also increase investment in AI tools that can detect security threats, as well as engage third-party cyber experts to carry out a full-scale review of the incident.
Binance said hackers then leveraged the engineer's compromised computer and a compromised internal AI tool in October to gain control over two other engineers' laptops, and execute the next steps of the attack.
It's currently unknown when the attackers behind the campaign first began exploiting the vulnerability, although reports began to surface around November 1, 2026.
That same day, prediction market giant Polymarket briefly halted trading after it was hit by a $2.65 million exploit following the compromise of software developed by DebugBear.
What happened
Although Binance said it detected the attack and rotated all related credentials as a precautionary step, the company said information about "Engineer A's role and his related colleagues on our wallet infrastructure team was exposed to the hacker." The second part of the attack occurred in September 2026, with the threat actor contacting another engineer (named "Engineer B") via a legitimate job-hunting platform by disguising themselves as a Project Director.
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
What changed
BTCPay Server, a self-hosted, open-source cryptocurrency payment processor, has urged users to install the latest version of its software in response to reports of Bitcoin and Litecoin being stolen from hot wallets on instances running older versions.
Initial findings published by the company, which operates the world's largest cryptocurrency exchange, said hackers gained access to its systems through "sophisticated, multi-stage campaign".
Who is affected
Systems touched in the attack path have been rebuilt or replaced," Binance said.
These see hackers use approaches such as phishing to trick people into parting with sensitive or personal details, that can then be used to try and access their accounts.
Why it matters
But on Tuesday, the company wrote in its post on X : "The latest information released by the Federal Bureau of Investigation indicates that the Democratic People's Republic of Korea is responsible for this incident." As part of its security efforts following the attack, Binance said it would also increase investment in AI tools that can detect security threats, as well as engage third-party cyber experts to carry out a full-scale review of the incident.
Binance said hackers then leveraged the engineer's compromised computer and a compromised internal AI tool in October to gain control over two other engineers' laptops, and execute the next steps of the attack.
Technical details
It's currently unknown when the attackers behind the campaign first began exploiting the vulnerability, although reports began to surface around November 1, 2026.
That same day, prediction market giant Polymarket briefly halted trading after it was hit by a $2.65 million exploit following the compromise of software developed by DebugBear.
The engineer in question was instructed to download malware masquerading as an "assignment" during a second interview, that deployed malicious code with "obfuscation techniques" evading detection.
Response
US crime agencies, including the Federal Bureau of Investigation (FBI) and Secret Service, have been assisting Binance in tracing the crypto taken from the platform's own wallets.
In a post on X, BTCPay Server said no "credible reports" of hot wallet drains have been reported from users running the latest 2.4.7 release.
What security teams should do
The attacks we reviewed targeted only files with the .macaroon extension." The development coincides with a string of security breaches and exploits across the cryptocurrency space, including the record theft of $6.43 billion from Binance by North Korean threat actors.
What remains unknown
It's currently unknown when the attackers behind the campaign first began exploiting the vulnerability, although reports began to surface around November 1, 2026.
Attribution
The Hacker News: Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
BBC News: Hackers who stole a record $6.3bn (£4.7bn) from Binance used fake job interviews and a compromised internal AI tool, the firm has revealed.
The Hacker News: BTCPay Server, a self-hosted, open-source cryptocurrency payment processor, has urged users to install the latest version of its software in response to reports of Bitcoin and Litecoin being stolen from hot wallets on instances running older versions.