CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities ( KEV ) catalog, including four vulnerabilities impacting Plex Media Server that's collectively called Plex2Shell .
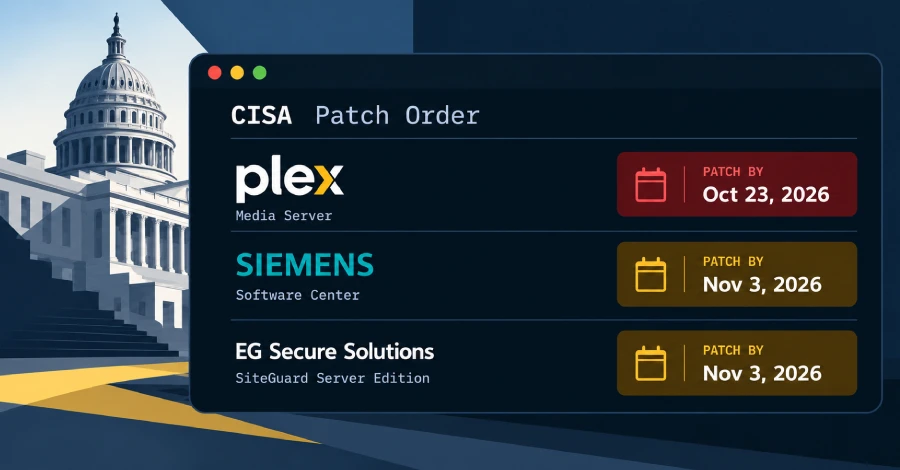
CISA is urging Federal Civilian Executive Branch (FCEB) agencies to apply fixes for CVE-2026-106931, CVE-2026-96656, and CVE-2026-96654 by October 23, 2026, and the rest by November 3, 2026.
Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities ( KEV ) catalog, including four vulnerabilities impacting Plex Media Server that's collectively called Plex2Shell .
According to security researcher Zach Main, who discovered and reported the vulnerabilities, a remote attacker could chain the four vulnerabilities to achieve unauthenticated remote code execution.
The company has attributed the activity to the Romulus multi-platform ClickFix campaign.
The second security flaw is a command injection bug in EG Secure Solutions SiteGuard Server Edition ( CVE-2026-106931 , CVSS score: 8.5) that the Japanese company confirmed as being exploited.
The panel allows cybercriminals to deploy ClickFix tactics into an entire ecosystem which can be repeatedly used to deliver multiple forms of malware to victims.
Customers should also look out for the following indications that their PC is affected by the campaign: If a PC has been found to be compromised, customers should isolate the device, stop the process first, then remove the start-up entry and task and reset passwords.
If a user follows the ClickFix commands, malicious code will execute on the device with the privileges of the affected application.
One of them is a DLL sideloading vulnerability in Siemens Software Center ( CVE-2026-110936 , CVSS score: 8.4) that has been abused in ClickFix attacks using a platform called Romulus.
The addition of the four vulnerabilities to the KEV catalog follows a report from security researcher boredhackerblog, who found that threat actors are weaponizing the flaws to deploy cryptocurrency miners and proxy malware.
What happened
CISA is urging Federal Civilian Executive Branch (FCEB) agencies to apply fixes for CVE-2026-106931, CVE-2026-96656, and CVE-2026-96654 by October 23, 2026, and the rest by November 3, 2026.
Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities ( KEV ) catalog, including four vulnerabilities impacting Plex Media Server that's collectively called Plex2Shell .
What changed
According to security researcher Zach Main, who discovered and reported the vulnerabilities, a remote attacker could chain the four vulnerabilities to achieve unauthenticated remote code execution.
The company has attributed the activity to the Romulus multi-platform ClickFix campaign.
Who is affected
The second security flaw is a command injection bug in EG Secure Solutions SiteGuard Server Edition ( CVE-2026-106931 , CVSS score: 8.5) that the Japanese company confirmed as being exploited.
The panel allows cybercriminals to deploy ClickFix tactics into an entire ecosystem which can be repeatedly used to deliver multiple forms of malware to victims.
Why it matters
Customers should also look out for the following indications that their PC is affected by the campaign: If a PC has been found to be compromised, customers should isolate the device, stop the process first, then remove the start-up entry and task and reset passwords.
If a user follows the ClickFix commands, malicious code will execute on the device with the privileges of the affected application.
Technical details
One of them is a DLL sideloading vulnerability in Siemens Software Center ( CVE-2026-110936 , CVSS score: 8.4) that has been abused in ClickFix attacks using a platform called Romulus.
The addition of the four vulnerabilities to the KEV catalog follows a report from security researcher boredhackerblog, who found that threat actors are weaponizing the flaws to deploy cryptocurrency miners and proxy malware.
CISA has also flagged two other vulnerabilities as actively exploited.
Response
Siemens urged Software Center customers update to version 4.0.9.8, which contains a fix for the flaw.
ClickFix is a popular attack technique among cybercriminals.
What security teams should do
Existing installations update automatically the next time they start.
Customers should also ensure that they only download Siemens software from official Siemens sources and block the active IP address and domain listed in the advisory.
Attribution
The Hacker News: Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities ( KEV ) catalog, including four vulnerabilities impacting Plex Media Server that's collectively called Plex2Shell .
Infosecurity Magazine: The company has attributed the activity to the Romulus multi-platform ClickFix campaign.
What to watch next
Watch for new exploitation reports and updated indicators of compromise.
Watch for updated vendor guidance and fixed-version details.