APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits
The Russia-linked threat actor known as APT29 is presumed to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker.
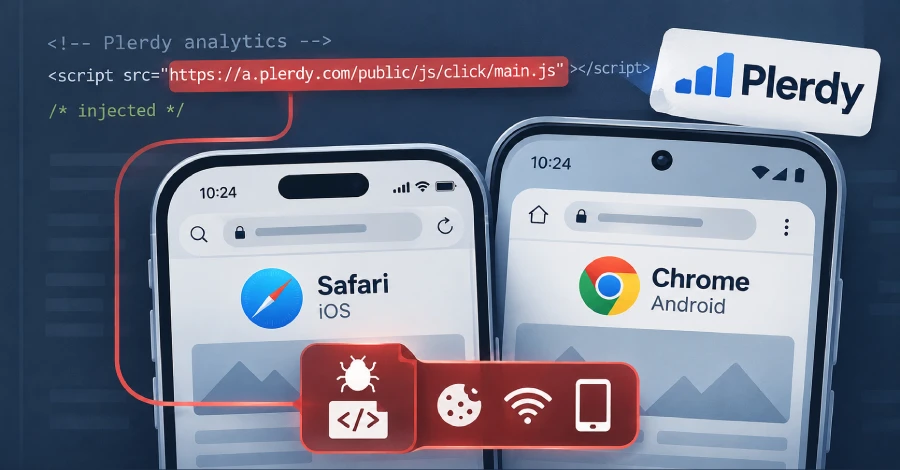
The Russia-linked threat actor known as APT29 is presumed to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker.
Sekoia researchers Amaury-Jacques Garçon and Félix Aime said in a technical report shared with the outlet.
A defining aspect of the campaign is the use of three infection vectors - Some of the compromised websites include a major industry trade association representing U.S. companies operating in the chemical industry, a far-right European political party, and a Bulgarian military-related website.
It's suspected that the watering hole campaign may have been designed to target specific individuals rather than a broad effort; no less than three different exploits have been identified - In all three cases, the exfiltrated data is sent to the endpoint.
The development comes weeks after iVerify and Report URI revealed that the P7 variant of DarkSword is being delivered via half-click attacks that leverage ad-based infrastructure.
However, several of these sites are likely to attract high-value or strategically important visitors in the context of the Russia-Ukraine war.
This supply chain attack spread through high-value targets, such as army, special forces, and military equipment (ballistic, UAV) websites. On Android, the malware is equipped to exfiltrate Chrome data and Wi-Fi passwords without establishing persistence.
Although Coruna was initially developed by a nation-state actor for highly targeted operations, its subsequent leak following initial disclosure has made the toolkit widely accessible to multiple threat actors for their own campaigns.
In one case, the exploit is said to have been propagated through a malicious Instagram ad themed around the World Cup and served from The other pathway is part of a criminal campaign dubbed DeadTag, in which attackers acquire expired domains behind old analytics and advertising tags that are still loaded by thousands of websites.
The iPhone exploit paths that take advantage of DeadTag lead to the Coruna exploit kit for older iPhones running iOS version 13 to 17.2.1 and DarkSword P7 for iOS devices running 18.4 to 18.7.
The Android attack chain incorporates a check to determine whether the targeted device is a Samsung Galaxy S25 Ultra by examining its model identifier (i.e., SM-S938B).
What happened
The Russia-linked threat actor known as APT29 is presumed to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker.
Sekoia researchers Amaury-Jacques Garçon and Félix Aime said in a technical report shared with the outlet.
A defining aspect of the campaign is the use of three infection vectors - Some of the compromised websites include a major industry trade association representing U.S. companies operating in the chemical industry, a far-right European political party, and a Bulgarian military-related website.
What changed
It's suspected that the watering hole campaign may have been designed to target specific individuals rather than a broad effort; no less than three different exploits have been identified - In all three cases, the exfiltrated data is sent to the endpoint.
The development comes weeks after iVerify and Report URI revealed that the P7 variant of DarkSword is being delivered via half-click attacks that leverage ad-based infrastructure.
Who is affected
However, several of these sites are likely to attract high-value or strategically important visitors in the context of the Russia-Ukraine war.
This supply chain attack spread through high-value targets, such as army, special forces, and military equipment (ballistic, UAV) websites. On Android, the malware is equipped to exfiltrate Chrome data and Wi-Fi passwords without establishing persistence.
Why it matters
Although Coruna was initially developed by a nation-state actor for highly targeted operations, its subsequent leak following initial disclosure has made the toolkit widely accessible to multiple threat actors for their own campaigns.
Technical details
In one case, the exploit is said to have been propagated through a malicious Instagram ad themed around the World Cup and served from The other pathway is part of a criminal campaign dubbed DeadTag, in which attackers acquire expired domains behind old analytics and advertising tags that are still loaded by thousands of websites.
The iPhone exploit paths that take advantage of DeadTag lead to the Coruna exploit kit for older iPhones running iOS version 13 to 17.2.1 and DarkSword P7 for iOS devices running 18.4 to 18.7.
Response
The Android attack chain incorporates a check to determine whether the targeted device is a Samsung Galaxy S25 Ultra by examining its model identifier (i.e., SM-S938B).
Attribution
The Hacker News: The Russia-linked threat actor known as APT29 is presumed to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker.
What to watch next
Watch for additional victim details, indicators of compromise and follow-on exploitation reports.